Welcome to WordPress. This is your first post. Edit or delete it, then start writing!
Blog
-
Untangling a Fragmented Digital Infrastructure
Situation
While providing data privacy and policy consultancy for a mid-sized tax and accounting firm, we discovered a significant operational bottleneck. The firm was trapped in a “digital net” created by their previous web design agency.
Their domain was registered on one platform, the website hosted on another, and professional emails managed on a third—all under the agency’s private accounts. This fragmentation meant the firm had zero direct access to their own assets, faced soaring “management fees,” and suffered from extreme delays whenever technical support was needed.
Task
The objective was to audit the firm’s entire digital footprint, establish clear ownership, and migrate their scattered services into a single, transparent, and high-performance environment. The client wanted to stop overpaying for “middleman” services and regain the ability to scale their digital presence without being held back by a third party.
Action
We executed a comprehensive transition plan focused on transparency and security:
-
Infrastructure Audit: We conducted a deep dive into their existing setup, identifying every service provider and uncovering hidden costs that weren’t being disclosed to the client.
-
Asset Reclamation: We managed the delicate process of transferring the domain and hosting credentials back into the accounting firm’s name, ensuring they held the “master keys” to their business.
-
Consolidated Migration: We migrated the website and all historical email data to a unified, secure hosting environment. This eliminated the need for three separate providers and streamlined their billing.
-
Modern Redesign: With the backend secured, we redesigned their website from the ground up to improve user experience, mobile responsiveness, and client-side content management.
-
Data Privacy Integration: We baked their new privacy policies and secure client portals directly into the new site architecture to ensure compliance.
Result
The transition resulted in a total digital transformation for the firm:
-
Ownership: The client now has 100% administrative control over their domain and hosting.
-
Cost Reduction: By removing unnecessary markups and consolidating providers, the firm reduced their annual digital overhead by approximately 40%.
-
Efficiency: Technical issues that previously took days to resolve are now handled in minutes through a direct support line.
-
Performance: Website loading speeds improved significantly, and the firm now has a modern platform that reflects their professional status in the accounting industry.
Key Takeaways
-
Transparency Over Marketing: Never choose a provider based on their ranking alone; choose them based on their willingness to give you full access to your own accounts.
-
Avoid Fragmented Hosting: Keeping your domain, email, and web hosting with too many different “hoisters” creates a web of dependency that is hard to escape.
-
Ownership is Non-Negotiable: Ensure your domain and accounts are registered in your company’s name from day one. If a designer refuses to give you admin access, it’s a red flag.
-
-
The Digital Web
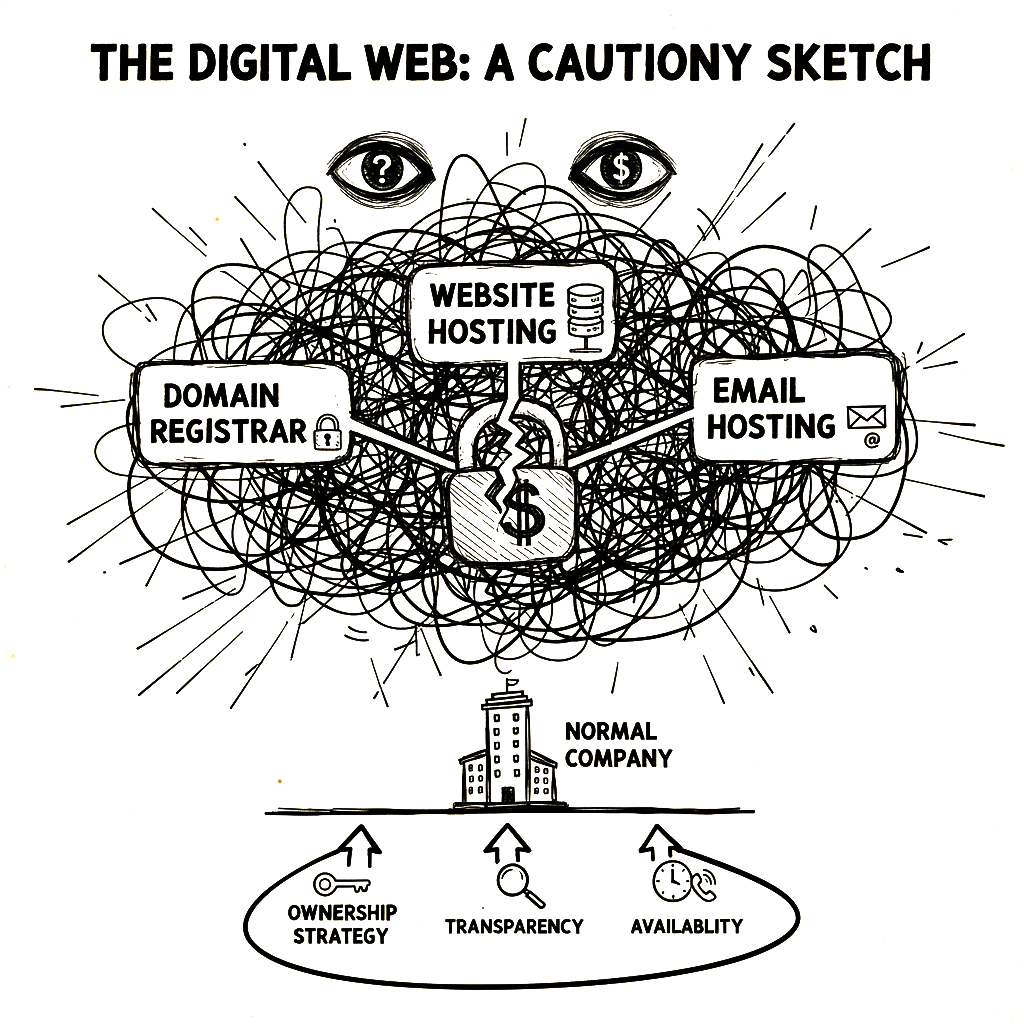
The Digital Web: Is Your Web Designer Setting You Up for a Headache?
When you hire a professional web design company, you’re looking for a partner to build your digital storefront. You expect a beautiful website, a smooth launch, and a boost in business. However, behind the scenes of a “pretty” site, a tangled web of technical decisions can sometimes leave a business owner feeling more like a hostage than a client.
One of the most common and frustrating issues we see in the IT world is infrastructure fragmentation. This happens when a design firm registers your domain on one platform, hosts your website on a second, and sets up your professional emails on a third.
While there are sometimes technical reasons for using different providers, this “net” of services often becomes an overwhelming mess for companies without a deep technical background.
The High Cost of the “Big Net”
For a normal business owner, managing three different logins, three different billing cycles, and three different support teams is exhausting. But the real problem isn’t just the admin it’s the dependency.
When your digital assets are scattered across various “hoisters” and registrars, you become fully dependent on the web designer to act as the middleman. If you want to move or change a service, you might find yourself:
-
Locked in: Realizing you don’t actually “own” your domain or have the master keys to your hosting.
-
Overpaying: Paying high “management fees” just to keep the fragmented pieces connected.
-
Stuck in the Middle: If your email goes down, the email host blames the domain settings, the domain provider blames the host, and you’re left losing money while they point fingers.
How to Choose a Partner (Not Just a Designer)
Your choice of a web designer shouldn’t be based solely on their flashy marketing or their Google ranking. A high ranking doesn’t always equal high transparency. Instead, look for these three pillars:
1. Ownership Strategy
Before signing anything, ask: “Who will own the domain account?” A transparent company will set up accounts in your name. You should always have the “Owner” or “Admin” credentials. If they insist on keeping everything in their agency account, they are creating a cage, not a service.
2. Transparency in Infrastructure
A good designer should be able to explain why they are choosing certain providers. If they are splitting your services across multiple platforms, they should provide a clear “Map of Assets” so you know exactly where everything lives and how much each piece costs.
3. Real-World Availability
The most important factor isn’t how the site looks on launch day, it’s what happens at 2:00 PM on a Tuesday when your checkout stops working. Test their responsiveness before you hire them. If they take three days to answer a sales inquiry, imagine how long they’ll take to fix a broken server.
The Bottom Line
A professional website should be an asset that empowers your business, not a complex web of services that drains your budget and keeps you in the dark. Don’t be afraid to ask the “dumb” questions about who owns what. A truly professional IT partner will be happy to explain it because they want you to stay for their quality of work, not because you’re trapped.
Is your current setup feeling a bit too complicated?
Would you like me to create a “Digital Asset Checklist” you can use to audit your current website and domain ownership?
Please let us know at : info@9aurastech.com
-
-
Enterprise Data Backup & Disaster Recovery (DR) Blueprint
Overview
Existing backup processes were ad hoc and did not meet industry compliance standards (ISO 22301).
Solution Overview
Backup Strategy Implemented a 3 2 1 policy – three copies of data, two on separate media types, one off site. Utilised Veeam Backup & Replication with Azure Blob Storage for the off site copy. Guarantees data durability and rapid recovery.
Retention & Compliance – Configured retention schedules (7 days daily, 30 days weekly, 365 days yearly) aligned to regulatory mandates. Added automated compliance reports via Veeam ONE. Provides audit trail for regulators and internal stakeholders.
Disaster Recovery Plan Designed a tiered DR site – primary data center, secondary on prem cluster, and cloud failover. Automated orchestrated switchover using Azure Site Recovery. Minimises downtime to <30 minutes under most scenarios.
Testing & Validation – Conducted monthly restore drills for critical applications (ERP, WMS) and logged results in the DR playbook. Updated the playbook after each test to reflect lessons learned. Builds confidence in the plan’s effectiveness.
Governance – Drafted a Data Protection Policy that outlines roles, responsibilities, and escalation paths during incidents. Trained IT staff on policy execution. Ensures accountability and reduces human error.
Outcome
-
The company now meets ISO 22301 certification requirements for business continuity.
-
Backup windows were reduced by 40 % through incremental backups and WAN acceleration.
-
During a simulated outage, the team restored core services in under 25 minutes, well within the agreed SLA.
Key Takeaway
-
Architecture first, policy second – A well planned infrastructure provides the foundation for all security, compliance, and performance gains.
-
Automation is key – From VPN provisioning to backup orchestration, automation reduces human error and frees up IT teams for strategic initiatives.
-
Governance drives trust – Clear policies, documented processes, and regular testing are what turn technical solutions into business level assurances.
-
-
Migrating Database to Microsoft SharePoint Online
Overview
Our client a Boutique Builders required a cloud based platform that could host their existing database, preserve all group policies, and support future expansion without locking the company into a single vendor.
Solution Overview
-
Governance Planning – Convened workshops with board members to define data ownership roles, retention schedules, and compliance checkpoints (GDPR, ISO 27001). Drafted a Data Governance Charter. Sets clear expectations and reduces legal risk.
-
SharePoint Architecture – Built a SharePoint Online tenant under the company’s microsoft 365 account. Created site collections for each business unit with unique permission levels. Enabled Content Types and Managed Metadata to enforce naming conventions. Provides granular control while leveraging Microsoft’s native compliance features.
-
Data Migration – Used Microsoft Power Automate + ShareGate to map relational tables into list structures, preserving relationships via lookup columns. Implemented incremental sync for real time updates during the transition window. Minimises downtime and ensures data integrity.
-
Future Proofing – Deployed a PowerApps front end for custom forms, integrated with Microsoft Power BI for reporting, and set up a SharePoint Framework (SPFx) web part to preview large datasets directly in the browser. Gives stakeholders immediate insight while keeping the platform extensible.
Outcome
-
99.7 % of records migrated with zero corruption.
-
The firm now enjoys automated backups, audit logs, and compliance reporting built into SharePoint.
-
Board members confirmed that the solution aligns with their strategic roadmap for digital transformation.
-
-
Turning Complex Challenges into Seamless Business Solutions
Overview
A Mid size designing and drafting agency (20-40 employees) needed a secure, on premises file sharing solution that would allow staff to work from home without compromising data integrity or compliance.
Solution Overview
-
Assessment & Design – Mapped the existing network topology and identified critical data assets. Designed a NAS architecture (Synology) with redundant power supplies, 10 GbE uplinks, and local SSD cache for performance. Provides a scalable foundation that can grow with user demand.
-
User & Group Policy – Created AD groups aligned to departmental roles (Marketing, Finance, HR, Engineer). Configured NTFS permissions on shared volumes to enforce least privilege access. Eliminates accidental data exposure while keeping collaboration fluid.
-
Authentication & VPN Installed – Windows Server 2019 as an Azure AD connected domain controller. Set up OpenVPN Server on the NAS and generated client profiles for every employee laptop, ensuring mutual TLS authentication. Guarantees that only verified users can reach the file server, regardless of location.
-
Deployment & Training – Rolled out VPN clients via Intune scripts, provided a quick start guide, and conducted a live demo session. Monitored connection logs for 48 hours to validate reliability. Reduces onboarding friction and builds confidence in remote access.
Outcome
-
98 % of staff connected within the first week, with zero reported data loss incidents.
-
VPN throughput remained above 90 Mbps on average, enabling smooth file transfers even during peak hours.
-
The agency’s IT team praised the solution for its “plug and play” nature and minimal maintenance overhead.
Key Takeaway
Choosing the right hardware is the most important and value added pactice for the client and reducing the clusters on premises.
-
-
The Small Business Owner’s Guide to Cybersecurity
Introduction
As a small business owner, you wear many hats—operations, sales, customer service—and cybersecurity is often another responsibility that gets added to your already full plate. However, with limited budgets and technical expertise, how do you implement meaningful security measures without getting overwhelmed by complex jargon or expensive solutions?
The Reality of Small Business Security
According to Verizon’s 2023 Data Breach Investigations Report:
-
43% of cyber attacks target small businesses
-
83% of those attacks are phishing-related
-
The average cost of a breach for SMEs is $57,000 USD (including downtime, recovery, and reputation damage)
But here’s the good news: you don’t need to be a technology expert or make massive investments to significantly improve your security posture.
Prioritizing Security Efforts
-
Protect What Matters Most
-
Identify your most critical assets (customer data, financial information, proprietary business data)
-
Focus initial efforts on protecting these high-value targets
-
-
Understand Your Threat Model
-
What types of attacks are most likely to target your industry?
-
Who within your organization might be most vulnerable to social engineering attempts?
-
-
Leverage Existing Security Measures
-
Many basic security practices (like strong passwords) provide significant protection
-
Focus on getting the basics right before investing in advanced solutions
-
Essential Security Protections for SMEs
-
Strong Authentication Practices
-
Implement multi-factor authentication (MFA) for all critical systems
-
Use password managers to generate and store complex passwords
-
Establish clear password policies and enforce regular changes
-
-
Endpoint Protection
-
Install reputable antivirus/anti-malware software on all devices
-
Keep all software updated, including operating systems and third-party applications
-
Implement device encryption for laptops and mobile devices
-
-
Secure Network Infrastructure
-
Use strong Wi-Fi encryption (WPA3) with unique passwords
-
Segment your network to limit potential attack spread
-
Consider using a business-grade firewall
-
-
Data Backup Strategy
-
Implement the 3-2-1 backup rule: three copies, two different media, one offsite
-
Test backups regularly to ensure they can be restored
-
Air gap your most critical data (keep it completely disconnected from the network)
-
-
Employee Security Training
-
Conduct regular security awareness training
-
Run phishing simulation tests quarterly
-
Establish clear policies for handling sensitive information
-
-
Vendor & Third-Party Risk Management
-
Assess the security posture of vendors with access to your systems
-
Limit third-party access using principles of least privilege
-
Include security requirements in contracts with service providers
-
When to Call in Professional Help
While you can implement many basic protections yourself, some situations warrant professional assistance:
-
If you lack internal IT expertise for complex implementations (like firewalls or advanced backup systems)
-
When dealing with specific compliance requirements (HIPAA, PCI DSS, etc.)
-
After a security incident to ensure proper investigation and remediation
-
For ongoing monitoring if your business handles particularly sensitive data
Creating a Security Culture
-
Lead by Example: As the owner, model good security practices for your team.
-
Make it Part of Onboarding: Include basic security training in new employee orientation.
-
Regular Refresher Training: Schedule quarterly sessions to reinforce best practices.
-
Encourage Reporting: Create safe channels for employees to report concerns or suspicious activity.
Affordable Security Solutions
-
Password Managers: $2-5 per user/month
-
Business-Grade Antivirus: Often included with business internet packages
-
Cloud Backup Solutions: Starting at $5/month for basic plans
-
MFA Services: Often free or low-cost through major providers
Building a Yearly Security Plan
-
January: Annual security assessment and training refreshers
-
April: Phishing simulation exercise (after Q2 tax rush)
-
July: Mid-year security review and policy updates
-
October: Cybersecurity awareness month activities with staff
-
December: End-of-year infrastructure review before holidays
Conclusion
Implementing effective cybersecurity doesn’t require technical expertise or large budgets—it begins with understanding your risks, prioritizing protective measures, and maintaining consistent practices.
-
-
Legacy Server Rescue
Situation
A client operated a critical, very old server running a proprietary application that could not be re installed on newer hardware. The existing server had reached end of life and was at risk of failure.
Task
Create a modern, supported environment that would host the legacy software without downtime or data loss.
Action
-
Assessment & backup – Took a full disk image of the legacy server (Windows 2008 R2) and stored it on an external NAS, ensuring no data loss during migration. Backup is essential before any virtualization or re installation attempt.
-
New physical host – Provisioned a fresh Windows Server 2022 Standard machine with 64 GB RAM, 4 TB SSD storage, and dual NICs for high availability. Modern hardware provides better performance and supports newer virtualization technologies.
-
Hyper V setup – Installed Hyper V role, created a virtual switch linked to the physical NIC, and configured VM resources (8 vCPU, 16 GB RAM). Allows isolation of legacy workloads while keeping them on a supported host.
-
Virtualized migration – Restored the disk image as a VHDX file within Hyper V, then ran the legacy application inside the VM. Adjusted registry keys and network settings to match the new environment. Keeps the application running in its native OS while leveraging modern hardware.
-
Testing & go live – Ran full functional tests, verified data integrity, and conducted a failover drill by moving the VM to a standby host. Ensures business continuity and validates the migration plan.
Result
-
The client’s critical application is now running on a fully supported platform with zero downtime during the transition.
-
Future maintenance is simplified—updates can be applied at the Hyper V level rather than each legacy server.
-
The client expressed high satisfaction, noting that the new setup has reduced their annual IT support costs by 30 %.
Key Takeaway
When you can’t reinstall a rare application on modern hardware, virtualizing it on a fresh host is often the most reliable and cost effective solution.
-
-
The Security Journey – Lessons from a Ransomware Recovery
Introduction
Ransomware attacks have become an unfortunate reality for businesses of all sizes, with small and medium-sized enterprises (SMEs) increasingly targeted due to perceived weaker defenses. One After Hours GP firm harrowing experience with a ransomware attack offers valuable lessons for other small businesses about prevention, response, and building a more secure future.
The Story: An After Hours GP Firm’s Ransomware Recovery
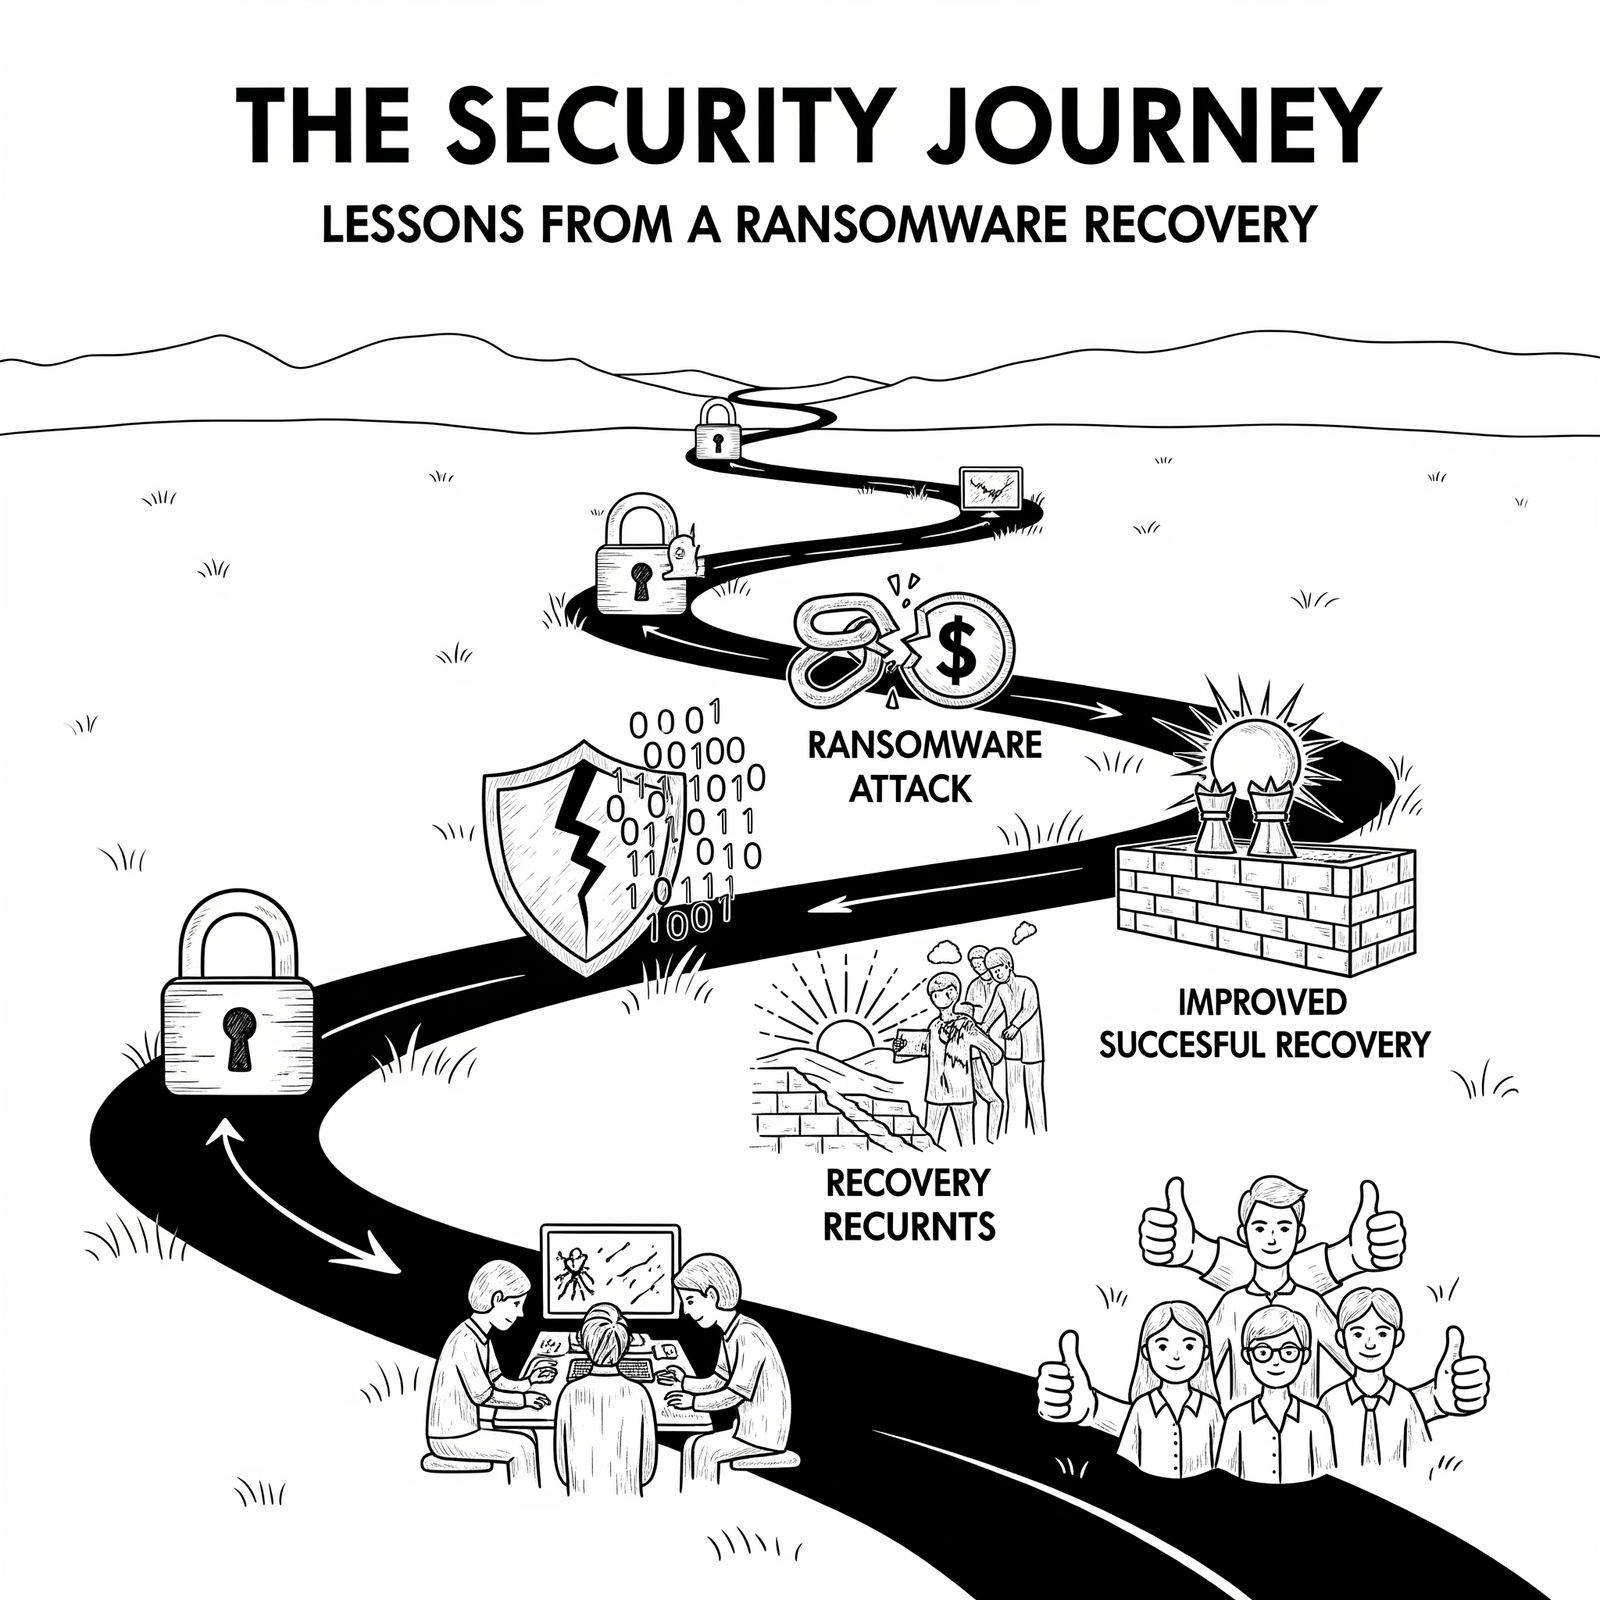
ABC After Hours GP firm (name changed for privacy) became victim to a sophisticated ransomware attack that encrypted critical client files and disabled their practice management system. Here’s what happened next:
-
Discovery: The firm noticed slow performance on Monday morning. By midday, they realized file extensions had been changed and systems were locked with a demand for cryptocurrency payment.
-
Immediate Response:
-
Disconnected affected machines from the network
-
Contacted their IT support provider (who unfortunately didn’t have comprehensive backup procedures in place)
-
Began notifying clients about potential data breaches
-
-
The Aftermath:
-
Client trust was severely damaged, with some high-profile cases threatening to leave
-
They spent a handsome amount on emergency IT services and legal fees related to the incident
-
Productivity ground to a halt for nearly two weeks while they rebuilt systems from scratch
-
Key Lessons for Small Businesses
-
You Are a Target
-
43% of cyber attacks target small businesses (Verizon DBIR)
-
Attackers know SMEs often have fewer resources to invest in security
-
You don’t need to be a high-profile company to be targeted
-
-
Prevention is Better Than Cure The firm’s lack of proper backups and network segmentation turned what might have been a minor incident into a major crisis.
-
Security Requires Investment While no solution guarantees 100% protection, basic measures could have mitigated the damage:
-
Regular, tested backups
-
Network segmentation to limit attack spread
-
Employee security training
-
Up-to-date endpoint protection
-
Building a Stronger Security Posture
-
Essential Security Layers
-
Firewall with intrusion prevention system (IPS)
-
Endpoint protection with behavior-based detection
-
Regular software updates and patch management
-
Multi-factor authentication for all critical systems
-
Secure backup solutions with air gap capabilities
-
-
Employee Training Programs
-
Conduct regular security awareness training
-
Run phishing simulation exercises quarterly
-
Create clear policies around password management and data handling
-
-
Incident Response Plan
-
Define roles and responsibilities for different scenarios
-
Document communication protocols with stakeholders (employees, clients, regulators)
-
Establish relationships with legal and PR experts beforehand
-
-
Continuous Monitoring
-
Implement SIEM (Security Information and Event Management) solutions if budget allows
-
Regular vulnerability scanning and penetration testing
-
Log analysis to detect anomalies early
-
Why Security Can Be a Competitive Advantage
-
Customer Trust: Demonstrating strong security practices can differentiate your business in crowded markets.
-
Business Continuity: Companies with robust security measures experience shorter downtimes after incidents.
-
Insurance Premiums: Better security posture often leads to lower cyber insurance costs.
-
Compliance Advantage: Proactive security implementation helps meet regulatory requirements for industries like healthcare and finance.
Where to Start
-
Conduct a basic security assessment (many SME-focused IT providers offer free assessments)
-
Implement “low-hanging fruit” fixes first (backups, MFA, endpoint protection)
-
Create an annual security improvement plan with measurable goals
-
Consider cyber insurance as part of your risk management strategy
Conclusion
The ABC firm’s story serves as a stark reminder that no business is immune from cyber threats—and reactive approaches often prove far more costly than proactive investments in security.
-
-
From Sluggish Internet to Seamless Connectivity
Situation
A client’s office network was plagued by intermittent connectivity and consistently low bandwidth. The IT team had already reset the existing router several times, but the issue persisted.
Task
Identify the root cause of the slow internet and implement a permanent, high performance solution.
Actions takens
-
Baseline measurement – Ran iperf3 tests between client PCs and an external server to quantify throughput; logged results at peak vs off peak hours. Provides objective data for troubleshooting.
-
Hardware inspection – Visited the office, inspected the router and modem. Found the router’s firmware was two years old and the modem had a known hardware defect that throttles downstream speeds below 50 Mbps. Outdated firmware often limits performance; defective modems can degrade throughput.
-
Router replacement – Deployed a new enterprise grade router with dual WAN support, QoS policies for VoIP and video conferencing, and integrated VPN capabilities. Modern routers provide better throughput, security, and manageability.
-
Modem upgrade recommendation – Advised the client to replace their modem with a newer model that supports DOCSIS 3.1, offering up to 300 Mbps downstream. Aligns the upstream bandwidth with the new router’s capacity.
-
Post deployment validation – Re ran iperf3, performed a full network health check, and confirmed QoS was prioritizing critical traffic. Ensures that the upgrade delivers real business value.
Outcome
-
Internet throughput increased from an average of 20 Mbps to 150 Mbps during peak hours.
-
VoIP call quality improved dramatically; jitter dropped below 5 ms.
-
The client reported a 90 % reduction in support tickets related to connectivity.
Key Takeaway
A router + modem combo can be the single most effective lever for improving office network performance, especially when the hardware is obsolete or defective.
-